Skip to the main content.

Our Communities

With over a decade of experience you can rely on us to help you solve the challenge of managing your supplier data.

  Buyer login

Defence, Aerospace & Security

Who We Help

We work with leaders across procurement, risk, resilience, and sustainability to manage supplier data, meet regulatory requirements, and strengthen their supply chains.

Suppliers

Welcome to the supplier community. Get support, find helpful resources, and explore innovative tools to streamline your reporting. 

  Supplier login

 Join Community 

Explore

With a comprehensive library of resources, feel free to explore and discover what you're looking for.

News and Updates

About

Explore Hellios, get to know our team, and discover exciting opportunities to join us. 

Inside the Buyer's Mind: Why Getting The Cyber Basics Right Builds Buyer Confidence
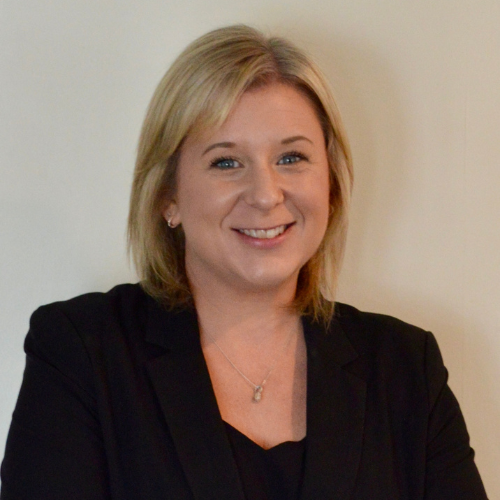
Claire Burgess, Procurement and Supply Chain Cyber Security Manager at MBDA and Chair of the JOSCAR Cyber Working Group

September 14, 2026 | 3 min read
Inside the buyers mind MBDA Hubspot

People often ask me if buyers actually use the cyber information suppliers provide through JOSCAR. The answer is we do, and probably more often than you think. 

It helps us understand supplier risk, identify where we might need further conversations and make informed decisions. But for that to work, the information needs to be accurate, up to date and completed by the right people. 

So, if I could give suppliers a few pieces of advice, these are the things I'd suggest they focus on. 

Keep your profile up to date

Sounds simple right? I know people are busy, but much can change in a year, especially when it comes to cyber security. That's why buyers look at a supplier’s JOSCAR profile consistently throughout the year. 

Using JOSCAR, I can quickly pull a report showing which suppliers have achieved Cyber Essentials, ISO27001 etc and where there may be gaps. That gives me an immediate picture of what's happening across the supply chain from a compliance perspective and potentially whether we need to have further conversations before a contract is awarded. 

If something changes, whether that's a new certification, stronger cyber controls or anything else, update your profile. Don't wait until renewal, be proud to show off what you have achieved and put in place. Buyers don't just look at your profile when it's time to renew; we rely on that information throughout the year. 

Make sure the right person fills it in

If there's one thing I'd encourage suppliers to do, it's make sure the right person completes the cyber section. 

If you can, involve the person responsible for cyber or IT security or a CISO if you have one. They'll understand the controls you have in place and be best placed to answer the questions accurately. 

If you're unsure about a question, don't guess. The Hellios and JOSCAR teams are there to support you. It's always better to ask than submit information that doesn't accurately reflect your organisation. 

The information you put into JOSCAR doesn't just sit there...we do actually use it! 

If it's not accurate, it's much harder for us to understand the level of risk or decide whether we need to ask more questions. The more confidence we have in the information, the more confidence we have in the supplier. 

Buyers really do work together  

I know JOSCAR can sometimes feel like just another questionnaire. But there is a reason we all ask the same questions. 

Buyers across the JOSCAR community have worked together to agree the information we need. Instead of every organisation asking suppliers slightly different questions, we've aligned around one set. That saves suppliers time and gives buyers more consistent information. 

Getting ahead of what’s coming next 

Cyber expectations aren't standing still; they're increasing all the time. Earlier this year, at CYBER UK the UK Government announced the Cyber Resilience Pledge, encouraging organisations to strengthen cyber resilience across their supply chains through wider adoption of Cyber Essentials. This was reinforced by Number 10 in July 2026 - the new Cyber Resilience Pledge comes as businesses face an increasingly urgent threat environment – with over 5 million cyber-crimes committed against UK firms last year, which is equivalent to 1 every 6 seconds (source: NCSC Annual Review 2025). 

My advice is to get ahead of those expectations now, rather than waiting until customers start asking for more. Organisations need to protect themselves from this ever-evolving threat and not just wait for contractual requirements. 

I'd also recommend taking a look at the National Cyber Security Centre's free Early Warning service. It's quick to set up, it's free, and it'll tell you if there are any obvious vulnerabilities you should know about. 

At the end of the day, JOSCAR isn't just about compliance. 

For me, it's about buyers working together to build stronger, more resilient supply chains. The better the information suppliers can give us, the better decisions we can make - and that's good for everyone.

Claire Burgess, Procurement and Supply Chain Cyber Security Manager at MBDA and Chair of the JOSCAR Cyber Working Group

September 14, 2026 | 3 min read